











How to use this page
Demo content. This page is a working reference for the ISMS Elements plugin. Nothing on it is a customer claim, a testimonial or a statistic about ISMS.online; ISO facts are the ones published on ISMS.online’s own ISO 27001 and ISO 42001 pages, and anything else is labelled as an example.
Every element below is a shortcode that works in the classic editor. Copy the code under an element into a page, change the text, and keep one item per line: fields on a line are separated by a vertical bar. The theme’s own shortcodes are listed after the elements.
Headings and summaries
Section head
An eyebrow, a large heading and a lead paragraph that open a major section of a guide. Use it where a long page changes subject, for example from the clauses to Annex A.
ISO 27001
An ISMS, in four themes
ISO/IEC 27001:2022 sets requirements in clauses 4 to 10 and lists 93 reference controls in Annex A.
[isms_section_head eyebrow="ISO 27001" heading="An ISMS, in four themes" level="3" toc="0"]
ISO/IEC 27001:2022 sets requirements in clauses 4 to 10 and lists 93 reference controls in Annex A.
[/isms_section_head]
Editable fields: eyebrow Eyebrow; heading Heading; inner content: Lead paragraph; level Heading level (2 or 3) (default 2); toc List the heading in “Jump to topic” (default on).
TL;DR summary strip
A short boxed summary at the top of a long guide: three to five points a reader can take away without scrolling.
TL;DR
- ISO/IEC 27001:2022 Annex A lists 93 controls in four themes.
- The requirements an ISMS is certified against are in clauses 4 to 10.
- The Statement of Applicability records which controls apply, and why.
- 11 of the 93 controls are new in the 2022 revision.
[isms_tldr heading="TL;DR"]
ISO/IEC 27001:2022 Annex A lists 93 controls in four themes.
The requirements an ISMS is certified against are in clauses 4 to 10.
The Statement of Applicability records which controls apply, and why.
11 of the 93 controls are new in the 2022 revision.
[/isms_tldr]
Editable fields: heading Heading (default In short); inner content: Points (one per line); columns Columns (1-2) (default 2).
Key claim line
One important, sourced statement set large with its source beside it. Use it for the single fact a page must land, such as a control count or a deadline.
Annex A controls were condensed from 114 to 93 in the 2022 revision.
[isms_keyline source="ISMS.online, ISO 27001 guide" source_url="https://www.isms.online/iso-27001/"]
Annex A controls were condensed from 114 to 93 in the 2022 revision.
[/isms_keyline]
Editable fields: inner content: Claim; source Source line; source_url Source URL; source_label Label on the source pill (default Source).
Beat lines
Short, punchy one-line statements that land a point between paragraphs. Use sparingly, no more than once or twice per page.
Scope it honestly.
Assess the risk, then choose the control.
Record the decision either way.
[isms_beat]
Scope it honestly.
Assess the risk, then choose the control.
Record the decision either way.
[/isms_beat]
Editable fields: inner content: Statements (one per line, use sparingly).
At-a-glance facts panel
Label and value rows summarising a standard, clause or control (edition, clauses, control count, deadlines). Put it near the top of a reference page.
ISO/IEC 27001:2022 at a glance
- Requirements
- Clauses 4 to 10
- Annex A controls
- 93, in four themes
- New in 2022
- 11 controls
- Published
- October 2022
[isms_facts heading="ISO/IEC 27001:2022 at a glance"]
Requirements | Clauses 4 to 10
Annex A controls | 93, in four themes
New in 2022 | 11 controls
Published | October 2022
[/isms_facts]
Editable fields: heading Heading (default At a glance); inner content: Facts: label | value (one per line).
Definition box
Defines one term, with its abbreviation and the clause it comes from. Use it the first time a page relies on a term such as Statement of Applicability.
Definition
Statement of ApplicabilitySoA
The document that lists the controls an organisation needs, says why each is included and whether it is implemented, and justifies any Annex A control it excludes.
Source: ISO/IEC 27001:2022, clause 6.1.3 d) (paraphrased)
[isms_definition term="Statement of Applicability" abbr="SoA" source="ISO/IEC 27001:2022, clause 6.1.3 d) (paraphrased)"]
The document that lists the controls an organisation needs, says why each is included and whether it is implemented, and justifies any Annex A control it excludes.
[/isms_definition]
Editable fields: kicker Kicker above the term (default Definition); term Term; abbr Abbreviation (optional); inner content: Definition; source Source line; source_url Source URL.
Callouts and quotes
Callout box
A boxed note in six types (info, tip, warning, success, note, important) for scope notes, audit tips and deadlines that must not be missed.
[isms_callout type="warning" title="Transition deadline"]
Certificates to ISO/IEC 27701:2019 must move to the 2025 edition before the transition period ends in October 2028.
[/isms_callout]
Editable fields: type Type — info, tip, warning, success, note, important (default info); title Title (defaults to the type name); inner content: Text.
Variant: type=”info”
[isms_callout type="info"]
Annex A controls are grouped into four themes: organisational, people, physical and technological.
[/isms_callout]
Variant: type=”tip”
[isms_callout type="tip" title="Audit tip"]
Record the justification for every excluded control in the Statement of Applicability.
[/isms_callout]
Variant: type=”success”
[isms_callout type="success" title="Example outcome"]
Example only: stage 1 closed with no major nonconformities.
[/isms_callout]
Variant: type=”note”
[isms_callout type="note"]
Clause numbers on this page follow ISO/IEC 27001:2022.
[/isms_callout]
Variant: type=”important”
[isms_callout type="important"]
Annex A is not the requirement set: the requirements are clauses 4 to 10.
[/isms_callout]
Pull quote
A short, attributable quotation set large, in mint, moss or plain. Only for real quotes with a named source.
Demo pull quote: use this for one short, attributable line from the article or an interview.
[isms_pull_quote cite="Demo attribution" role="Role, organisation"]
Demo pull quote: use this for one short, attributable line from the article or an interview.
[/isms_pull_quote]
Editable fields: inner content: Quote; cite Who said it; role Role / organisation; source_url Source URL (optional); source_label Source link label (default Source); tone Tone — mint, moss, plain (default mint).
Variant: tone=”moss”
Demo pull quote on the dark moss surface.
[isms_pull_quote tone="moss" cite="Demo attribution" role="Role, organisation"]
Demo pull quote on the dark moss surface.
[/isms_pull_quote]
Glossary tooltip (inline)
Marks a term inside a sentence and shows its definition on hover, tap or keyboard focus, so readers are not sent away from the page.
Every certified ISMS keeps an up-to-date SoAStatement of Applicability: the list of necessary controls with the justification for each. alongside its risk treatment plan.
<p>Every certified ISMS keeps an up-to-date [isms_term tip="Statement of Applicability: the list of necessary controls with the justification for each."]SoA[/isms_term] alongside its risk treatment plan.</p>Editable fields: inner content: Term; tip Definition shown in the tooltip.
Fact placeholder (inline)
A dashed marker for a number that is still being verified while a page is drafted. It must be replaced before the page is published.
Draft copy: [ — ] controls in scope after the next risk assessment.
<p>Draft copy: [isms_fact][ — ] controls in scope[/isms_fact] after the next risk assessment.</p>Editable fields: inner content: Placeholder text; note Hover note (default Placeholder: not yet verified).
Review card
Star rating, quote and attribution. Only for real, attributable customer reviews that have been approved for use.
Demo placeholder: replace with a real, attributable customer quote before this element is used on a live page.
[isms_review name="Customer name" company="Role, organisation" stars="5"]
Demo placeholder: replace with a real, attributable customer quote before this element is used on a live page.
[/isms_review]
Editable fields: inner content: Quote; name Name; company Company / role; stars Stars (1-5) (default 5); photo Photo (media ID).
Expertise band
Introduces the named expert who wrote or reviewed the page, with role, short bio and credentials, to show who stands behind the content.
Demo expert nameRole, organisation
Demo content: a short, verifiable bio of the person who wrote or reviewed the page. Replace before use.
- Credential one
- Credential two
- Area of practice
[isms_expertise name="Demo expert name" role="Role, organisation" initials="DE" creds="Credential one|Credential two|Area of practice"]
Demo content: a short, verifiable bio of the person who wrote or reviewed the page. Replace before use.
[/isms_expertise]
Editable fields: name Name; role Role / organisation; inner content: Bio; creds Credentials (one attribute split on |); photo Photo (media ID); initials Initials when there is no photo.
Reassurance bar
One reassuring line beside a shield icon, placed just before a call to action to answer the last objection.
[isms_risk_bar]
Demo content: this page is a layout test for the ISMS Elements plugin. Nothing here is a customer claim.
[/isms_risk_bar]
Editable fields: inner content: Reassurance text.
Lists and checklists
Tick list
A list with coloured tick, arrow, cross or dot icons, in one or two columns. “Term: text” lines make the term bold, useful for control or document lists.
[isms_ticklist color="mint" icon="tick"]
Scope: what the ISMS covers, and what it deliberately leaves out.
Risk assessment: how risks are identified, owned and evaluated.
Statement of Applicability: the applicable controls, with justifications.
[/isms_ticklist]
Editable fields: inner content: Items (one per line; “Term: rest” makes the term bold); color Icon colour — mint, blue, moss, orange, red, grey (default mint); icon Icon — tick, arrow, cross, dot (default tick); columns Columns (1-2) (default 1).
Variant: color=”blue” icon=”arrow” columns=”2″
[isms_ticklist color="blue" icon="arrow" columns="2"]
Organisational: 37 controls, 5.1 to 5.37.
People: 8 controls, 6.1 to 6.8.
Physical: 14 controls, 7.1 to 7.14.
Technological: 34 controls, 8.1 to 8.34.
[/isms_ticklist]
Numbered steps
A numbered how-to sequence with a bold title and one line of detail per step, joined by a line. Use it for implementation or certification steps.
- Define the scope
Set the boundaries of the ISMS and the interested parties (clause 4).
- Assess and treat risk
Identify risks, choose treatments, produce the Statement of Applicability (clause 6).
- Audit and review
Internal audit and management review before the certification audit (clauses 9 and 10).
[isms_steps]
Define the scope | Set the boundaries of the ISMS and the interested parties (clause 4).
Assess and treat risk | Identify risks, choose treatments, produce the Statement of Applicability (clause 6).
Audit and review | Internal audit and management review before the certification audit (clauses 9 and 10).
[/isms_steps]
Editable fields: heading Heading (optional); inner content: Steps: title | text (one per line).
Layer ladder
Connected, numbered rungs where each builds on the last and the final goal rung is filled. Use it for hierarchies such as policy, procedure and record.
- PolicyWhat the organisation commits to.
- ProcedureHow the commitment is met.
- Work instructionWho does what, step by step.
- RecordEvidence that it happened: what an auditor samples.
[isms_ladder]
Policy | What the organisation commits to.
Procedure | How the commitment is met.
Work instruction | Who does what, step by step.
Record | Evidence that it happened: what an auditor samples.
[/isms_ladder]
Editable fields: heading Heading (optional); inner content: Rungs: label | text (one per line); goal Goal rung — last, first, none (default last).
Requirement checklist
A checklist readers can tick off, with a running count remembered in their browser. Use it for readiness or audit-preparation lists.
Stage 1 readiness (example)
0 of 4 done
- ISMS scope documented and approvedclause 4.3
- Information security policy publishedclause 5.2
- Risk assessment and treatment completeclauses 6.1.2 and 6.1.3
- Statement of Applicability approvedclause 6.1.3 d)
[isms_checklist heading="Stage 1 readiness (example)"]
ISMS scope documented and approved | clause 4.3
Information security policy published | clause 5.2
Risk assessment and treatment complete | clauses 6.1.2 and 6.1.3
Statement of Applicability approved | clause 6.1.3 d)
[/isms_checklist]
Editable fields: heading Heading (optional); inner content: Items: item | note (one per line); remember Remember ticks in this browser (default on); of_label Progress wording: “2 of 4 done” (default of); done_label Progress wording: “2 of 4 done” (default done).
Big-number facts
A large figure beside the sentence that explains it, for two to four key numbers such as control counts.
- 93Annex A controls in ISO/IEC 27001:2022.
- 7clauses (4 to 10) hold the requirements an ISMS is audited against.
- 11controls are new in the 2022 revision.
[isms_big_numbers]
93 | Annex A controls in ISO/IEC 27001:2022.
7 | clauses (4 to 10) hold the requirements an ISMS is audited against.
11 | controls are new in the 2022 revision.
[/isms_big_numbers]
Editable fields: inner content: Facts: value | text (one per line).
Reference list
Rows of clause, control or document references, each with a badge, title and optional tag such as Required. Use it for mandatory documents or control lists.
Mandatory documented information (selection)
- 4.3Scope of the ISMSRequired
- 5.2Information security policyRequired
- 6.1.3Statement of ApplicabilityControls, justifications and implementation status.Required
- 9.2Internal audit programme and resultsRequired
[isms_ref_list heading="Mandatory documented information (selection)"]
4.3 | Scope of the ISMS | | Required
5.2 | Information security policy | | Required
6.1.3 | Statement of Applicability | Controls, justifications and implementation status. | Required
9.2 | Internal audit programme and results | | Required
[/isms_ref_list]
Editable fields: heading Heading (optional); inner content: Rows: ref | title | text | tag (one per line).
Key dates
Date tiles beside short descriptions for publication dates, transition deadlines and regulatory milestones.
- Oct 2022ISO/IEC 27001:2022 publishedAnnex A reorganised into four themes.
- Oct 2025ISO/IEC 27701:2025 publishedNew certifications can be issued against either edition.
- Oct 2028ISO/IEC 27701 transition endsCertificates to the 2019 edition move to the 2025 edition.
[isms_key_dates]
Oct 2022 | ISO/IEC 27001:2022 published | Annex A reorganised into four themes.
Oct 2025 | ISO/IEC 27701:2025 published | New certifications can be issued against either edition.
Oct 2028 | ISO/IEC 27701 transition ends | Certificates to the 2019 edition move to the 2025 edition.
[/isms_key_dates]
Editable fields: heading Heading (optional); inner content: Dates: when | title | text (one per line).
Glossary list
Terms and short plain-English definitions in two columns. Use it on guides that introduce several terms at once.
Paraphrased; ISO/IEC 27000 holds the normative vocabulary
- ISMS
- Information security management system: the policies, processes and controls an organisation uses to manage information security risk.
- Risk owner
- The person with the accountability and authority to manage a risk.
- Nonconformity
- A requirement that is not fulfilled.
[isms_glossary heading="Paraphrased; ISO/IEC 27000 holds the normative vocabulary"]
ISMS | Information security management system: the policies, processes and controls an organisation uses to manage information security risk.
Risk owner | The person with the accountability and authority to manage a risk.
Nonconformity | A requirement that is not fulfilled.
[/isms_glossary]
Editable fields: heading Heading (optional); inner content: Terms: term | definition (one per line).
Chips
A row of small rounded labels, optionally with a status dot, for topics, standards or clauses a section covers.
- ISO/IEC 27001:2022
- Annex A
- Statement of Applicability
- Risk treatment
[isms_chips tone="mint"]
ISO/IEC 27001:2022
Annex A
Statement of Applicability
Risk treatment
[/isms_chips]
Editable fields: inner content: Chips (one per line); tone Tone — neutral, mint, blue (default neutral); dot Show status dot (default on).
Variant: tone=”blue” dot=”0″
- Clause 4 Context
- Clause 6 Planning
- Clause 9 Performance evaluation
[isms_chips tone="blue" dot="0"]
Clause 4 Context
Clause 6 Planning
Clause 9 Performance evaluation
[/isms_chips]
Tags
Square-cornered labels in five tones for clause, control and status references (for example “New in 2022”).
[isms_tags]
mint: Clause 6.1.3
blue: Annex A 5.7
yellow: New in 2022
red: Nonconformity
grey: ISO/IEC 27002:2022
[/isms_tags]
Editable fields: inner content: Tags: tone: label (one per line; tones mint, blue, yellow, red, grey).
Sources list
A numbered list of sources with publisher and year, placed at the end of a page that cites standards or research.
Sources
- ISO 27001: the ultimate guide
- ISO 27001:2022 Annex A explained
- ISO/IEC 27001:2022 Information security management systems: Requirements
[isms_citations]
ISO 27001: the ultimate guide | ISMS.online | | https://www.isms.online/iso-27001/
ISO 27001:2022 Annex A explained | ISMS.online | | https://www.isms.online/iso-27001/annex-a-2022/
ISO/IEC 27001:2022 Information security management systems: Requirements | ISO/IEC | 2022 |
[/isms_citations]
Editable fields: heading Heading (default Sources); inner content: Sources: title | publisher | year | url (one per line).
Comparisons and tables
Two-up cards
Two side-by-side cards comparing a pair of concepts, each with a kicker, heading and paragraph (for example requirements versus controls).
Clauses 4 to 10
The requirements
What an organisation must do to run an ISMS, and what the certification auditor checks.
Annex A
The reference controls
93 controls to compare against when treating risk, recorded in the Statement of Applicability.
[isms_two_up left_kicker="Clauses 4 to 10" left_heading="The requirements" left_text="What an organisation must do to run an ISMS, and what the certification auditor checks." right_kicker="Annex A" right_heading="The reference controls" right_text="93 controls to compare against when treating risk, recorded in the Statement of Applicability."]Editable fields: left_kicker Left kicker; left_heading Left heading; left_text Left text; right_kicker Right kicker; right_heading Right heading; right_text Right text.
Do and don’t columns
Two columns of do and don’t items with tick and cross icons, for good and bad practice.
Do
- Record why each control applies
- Name a risk owner and keep it current
- Keep the Statement of Applicability with the risk assessment
Don’t
- Adopt a control set without assessing risk
- Leave an exclusion without a justification
- Treat Annex A as a checklist to tick
[isms_contrast left_heading="Do" right_heading="Don’t" left_items="Record why each control applies|Name a risk owner and keep it current|Keep the Statement of Applicability with the risk assessment" right_items="Adopt a control set without assessing risk|Leave an exclusion without a justification|Treat Annex A as a checklist to tick"]Editable fields: left_heading Left heading (default Do); left_items Left items (one per line, or one attribute split on |); right_heading Right heading (default Don’t); right_items Right items (one per line, or one attribute split on |).
Pros and cons
Plus and minus columns for weighing an option, such as an integrated management system.
Example: 27001 and 42001 together
- One internal audit programme can plan audits for both
- Shared document control and management review
Watch out for
- Scopes and risk criteria still differ
- AI impact assessments are an extra step
[isms_pros_cons pros_heading="Example: 27001 and 42001 together" pros="One internal audit programme can plan audits for both|Shared document control and management review" cons_heading="Watch out for" cons="Scopes and risk criteria still differ|AI impact assessments are an extra step"]Editable fields: pros_heading Pros heading (default Pros); pros Pros (one attribute split on |); cons_heading Cons heading (default Cons); cons Cons (one attribute split on |).
Myth vs fact
Common misconceptions set against the facts, row by row. Useful for correcting beliefs about audits and Annex A.
Myth
Every Annex A control must be implemented.
Fact
Controls are chosen through risk treatment; an exclusion is allowed when it is justified in the Statement of Applicability.
Myth
Annex A is the requirement set.
Fact
The requirements are clauses 4 to 10; Annex A is the reference set of controls.
[isms_myth_fact]
Every Annex A control must be implemented. | Controls are chosen through risk treatment; an exclusion is allowed when it is justified in the Statement of Applicability.
Annex A is the requirement set. | The requirements are clauses 4 to 10; Annex A is the reference set of controls.
[/isms_myth_fact]
Editable fields: inner content: Rows: myth | fact (one per line); myth_label Myth label (default Myth); fact_label Fact label (default Fact).
Versus comparison
A head-to-head comparison of two standards or approaches, row by row, that stacks on mobile. Use it on “A vs B” pages.
| Aspect | ISO/IEC 27001:2022 | ISO/IEC 42001:2023 |
|---|---|---|
| Management system for | Information security | Artificial intelligence |
| Edition | 2022 | 2023 |
| Certification | Yes | Yes |
[isms_versus left="ISO/IEC 27001:2022" right="ISO/IEC 42001:2023"]
Management system for | Information security | Artificial intelligence
Edition | 2022 | 2023
Certification | Yes | Yes
[/isms_versus]
Editable fields: left Left name; right Right name; aspect_label First column label (screen readers) (default Aspect); vs_label Badge between the two names (default vs); inner content: Rows: aspect | left | right (one per line).
Data table
A styled table whose first line is the header; yes, no and partial become icons and rows become cards on mobile. Use it for control or clause data.
| Theme | Controls | Range | New controls in 2022 |
|---|---|---|---|
| Organisational | 37 | 5.1–5.37 | yes |
| People | 8 | 6.1–6.8 | no |
| Physical | 14 | 7.1–7.14 | yes |
| Technological | 34 | 8.1–8.34 | yes |
Source: ISMS.online, Annex A controls (ISO/IEC 27001:2022)
[isms_table caption="Annex A themes in ISO/IEC 27001:2022" highlight="2" source="Source: ISMS.online, Annex A controls (ISO/IEC 27001:2022)"]
Theme | Controls | Range | New controls in 2022
Organisational | 37 | 5.1–5.37 | yes
People | 8 | 6.1–6.8 | no
Physical | 14 | 7.1–7.14 | yes
Technological | 34 | 8.1–8.34 | yes
[/isms_table]
Editable fields: caption Caption; highlight Highlight column (1-based, 0 = none); source Source note; inner content: Rows: cell | cell | cell (first line = header).
Mapping crosswalk
Maps items from one version or standard to another with a note per row, for example 2013 to 2022 controls.
| ISO/IEC 27001:2013 | maps to | ISO/IEC 27001:2022 | Change |
|---|---|---|---|
| A.5.1.1, A.5.1.2 | 5.1 Policies for information security | merged | |
| A.12.6.1, A.18.2.3 | 8.8 Management of technical vulnerabilities | merged | |
| No equivalent | 5.7 Threat intelligence | new |
[isms_mapping from_label="ISO/IEC 27001:2013" to_label="ISO/IEC 27001:2022"]
A.5.1.1, A.5.1.2 | 5.1 Policies for information security | merged
A.12.6.1, A.18.2.3 | 8.8 Management of technical vulnerabilities | merged
 | 5.7 Threat intelligence | new
[/isms_mapping]
Editable fields: from_label From column label (default ISO/IEC 27001:2013); to_label To column label (default ISO/IEC 27001:2022); none_label Shown when “from” is empty (default No equivalent); note_label Note column label (screen readers) (default Change); inner content: Rows: from | to | note (one per line; empty from = new).
Applies / does not apply cards
Two cards listing when something applies and when it does not, such as when a control can be excluded.
Annex A applies when…
- A risk assessment identifies the risk it treats
- The control is in scope for the ISMS
It can be excluded when…
- No identified risk needs it
- The justification is recorded in the Statement of Applicability
[isms_fit yes_heading="Annex A applies when…" yes_items="A risk assessment identifies the risk it treats|The control is in scope for the ISMS" no_heading="It can be excluded when…" no_items="No identified risk needs it|The justification is recorded in the Statement of Applicability"]Editable fields: yes_heading Fit heading (default A fit if you…); yes_items Fit items (one per line, or one attribute split on |); no_heading Not-a-fit heading (default Not a fit if you…); no_items Not-a-fit items (one per line, or one attribute split on |).
Compare card
A single card with a tag line, name, headline value, feature list and optional button, for describing one option or stage.
Certification auditStage 2
Implementation audit
On site or remote
- Tests the ISMS in operation
- Samples records and evidence
- Findings raised as nonconformities
[isms_compare_card title="Certification audit" note="Stage 2" name="Implementation audit" price="On site or remote" highlight="1" button_label="Certification guide" button_url="https://www.isms.online/iso-27001/certification/"]
Tests the ISMS in operation
Samples records and evidence
Findings raised as nonconformities
[/isms_compare_card]
Editable fields: title Tag line (top left); note Note (top right); name Name; price Headline value; price_note Headline note; inner content: Features (one per line); button_label Button label (optional); button_url Button URL; highlight Highlight this card (default off).
Standards and controls
Control card
A reference card for one Annex A control or clause: number badge, theme, summary, tags and a link to the full guide.
Annex A · Organisational
Threat intelligence
Collect and analyse information about information security threats to produce threat intelligence.
Read the control guide[isms_control_card ref="5.7" title="Threat intelligence" theme="Annex A · Organisational" tags="Organisational control|New in 2022" url="https://www.isms.online/iso-27001/annex-a-2022/5-7-threat-intelligence-2022/"]
Collect and analyse information about information security threats to produce threat intelligence.
[/isms_control_card]Editable fields: ref Reference (e.g. 5.7); title Title; theme Theme / clause group; inner content: Summary; tags Tags (one attribute split on |); url Link URL (optional); link_label Link label (default Read the control guide).
Gate rows
Readiness rows with pass, warn or fail pills, or yes and no icons, for showing what is and is not in place.
Readiness gates (example)
- PassScope defined and approved
- WarnRisk assessment completetwo risks still unowned
- FailInternal audit completescheduled, not yet run
[isms_gates heading="Readiness gates (example)"]
Scope defined and approved | pass
Risk assessment complete | warn | two risks still unowned
Internal audit complete | fail | scheduled, not yet run
[/isms_gates]
Editable fields: heading Heading (optional); inner content: Rows: label | status | note (status = pass, warn, fail, yes or no); style Style — pills, icons (default pills); status_labels Status words for pass, warn, fail (split on |) (default Pass|Warn|Fail).
Variant: style=”icons”
[isms_gates style="icons"]
Justify every exclusion | yes | The Statement of Applicability records why a control does not apply.
Name a risk owner | yes | Every risk has one person accountable for it.
Copy another organisation’s control set | no | Controls follow your own risk assessment.
[/isms_gates]
RACI matrix
A table of who is Responsible, Accountable, Consulted and Informed for each ISMS activity, with a legend.
| Activity | Top management | ISMS manager | Risk owner | Internal auditor |
|---|---|---|---|---|
| Approve the information security policy | A | R | C | I |
| Assess and treat a risk | I | A | R | C |
| Run the internal audit programme | I | A | C | R |
- RResponsible
- AAccountable
- CConsulted
- IInformed
[isms_raci roles="Top management|ISMS manager|Risk owner|Internal auditor" caption="Example allocation, not a recommendation"]
Approve the information security policy | A | R | C | I
Assess and treat a risk | I | A | R | C
Run the internal audit programme | I | A | C | R
[/isms_raci]
Editable fields: roles Roles (one attribute split on |); caption Caption; inner content: Rows: activity | R | A | C | I (one cell per role); activity_label First column label (default Activity); legend Legend words for R, A, C, I (split on |) (default Responsible|Accountable|Consulted|Informed).
Maturity model
Levels from initial to optimised, with the current level highlighted. Use it for self-assessment and roadmap pages.
Example maturity scale
- 1InitialAd hoc, undocumented.
- 2RepeatableDone the same way, informally.
- 3DefinedDocumented and approved.Current
- 4ManagedMeasured against objectives.
- 5OptimisedImproved from measurement.
[isms_maturity heading="Example maturity scale" current="3"]
1 | Initial | Ad hoc, undocumented.
2 | Repeatable | Done the same way, informally.
3 | Defined | Documented and approved.
4 | Managed | Measured against objectives.
5 | Optimised | Improved from measurement.
[/isms_maturity]
Editable fields: heading Heading (optional); current Current level (0 = none); current_label Badge on the current level (default Current); inner content: Levels: level | name | text (one per line).
Risk and process
Risk heat map
A likelihood-by-impact grid with banded scores and plotted risks, for explaining risk assessment and treatment.
Likelihood
| 5 | 5 Medium | 10 High | 15 High | 20 Critical | 25 Critical |
|---|---|---|---|---|---|
| 4 | 4 Low | 8 Medium | 12R1 High | 16 High | 20 Critical |
| 3 | 3 Low | 6 Medium | 9 Medium | 12 High | 15 High |
| 2 | 2 Low | 4 Low | 6 Medium | 8 Medium | 10R2 High |
| 1 | 1 Low | 2R3 Low | 3 Low | 4 Low | 5 Medium |
| 1 | 2 | 3 | 4 | 5 |
Impact
- Low
- Medium
- High
- Critical
[isms_heatmap marks="4,3:R1|2,5:R2|1,2:R3" caption="Example 5 x 5 risk matrix with three plotted risks (not a real assessment)"]Editable fields: size Grid size (3-5) (default 5); x_label Horizontal axis label (default Impact); y_label Vertical axis label (default Likelihood); marks Risks: likelihood,impact:label separated by | (e.g. 4,3:R1|2,5:R2); caption Caption; bands Band names, low to high (split on |) (default Low|Medium|High|Critical).
Plan-Do-Check-Act cycle
A four-stage cycle around a centre label, for continual-improvement models such as PDCA.
Plan-Do-Check-Act, one way to read clauses 6 to 10
Plan
Scope, objectives, risk assessment (clause 6).
Do
Operate the controls (clause 8).
Check
Monitor, audit, review (clause 9).
Act
Correct and improve (clause 10).
Continual improvement
[isms_cycle heading="Plan-Do-Check-Act, one way to read clauses 6 to 10"]
Plan | Scope, objectives, risk assessment (clause 6).
Do | Operate the controls (clause 8).
Check | Monitor, audit, review (clause 9).
Act | Correct and improve (clause 10).
[/isms_cycle]
Editable fields: heading Heading (optional); centre Centre label (default Continual improvement); inner content: Stages: label | text (one per line, 3-6).
Process pipeline
A row of numbered stage cards for a short process, such as identify, analyse, evaluate and treat.
Risk assessment and treatment
- 1IdentifyRisks to confidentiality, integrity and availability.
- 2AnalyseConsequences and likelihood.
- 3EvaluateAgainst the risk criteria.
- 4TreatChoose options and controls.
[isms_pipeline heading="Risk assessment and treatment"]
Identify | Risks to confidentiality, integrity and availability.
Analyse | Consequences and likelihood.
Evaluate | Against the risk criteria.
Treat | Choose options and controls.
[/isms_pipeline]
Editable fields: heading Heading (optional); inner content: Stages: label | text (one per line).
Relationship graph
A hub-and-spoke diagram showing how standards or concepts relate to one central item; a plain list on mobile and without JavaScript.
ISO/IEC 27001
- ISO/IEC 27002Control guidance
- ISO/IEC 27005Risk management guidance
- ISO/IEC 27017Cloud security controls
- ISO/IEC 27018PII in public clouds
- ISO/IEC 27701Privacy information management
- ISO/IEC 42001AI management systems
[isms_graph centre="ISO/IEC 27001" caption="Standards that build on or sit beside ISO/IEC 27001"]
ISO/IEC 27002 | Control guidance
ISO/IEC 27005 | Risk management guidance
ISO/IEC 27017 | Cloud security controls
ISO/IEC 27018 | PII in public clouds
ISO/IEC 27701 | Privacy information management
ISO/IEC 42001 | AI management systems
[/isms_graph]
Editable fields: centre Centre node; inner content: Nodes: label | note (one per line, up to 8); caption Caption.
Timeline
A vertical rail of dated or staged events, or a horizontal track with arrows. Use it for audit cycles and standard histories.
- Stage 1Documentation review
The auditor checks the ISMS documentation, scope and Statement of Applicability.
- Stage 2Implementation audit
The auditor tests whether the ISMS works as documented.
- SurveillancePeriodic audits
Sampled checks that the ISMS is still operating and improving.
- RecertificationFull audit
A complete audit before the certificate is reissued.
[isms_timeline]
Stage 1 | Documentation review | The auditor checks the ISMS documentation, scope and Statement of Applicability.
Stage 2 | Implementation audit | The auditor tests whether the ISMS works as documented.
Surveillance | Periodic audits | Sampled checks that the ISMS is still operating and improving.
Recertification | Full audit | A complete audit before the certificate is reissued.
[/isms_timeline]
Editable fields: inner content: Events: label | title | text | image URL (one per line); layout Layout — vertical, horizontal (default vertical).
Variant: layout=”horizontal” (arrow-driven)
- 2013ISO/IEC 27001:2013
Annex A: 114 controls.
- Oct 2022ISO/IEC 27001:2022
Annex A: 93 controls in four themes, 11 of them new.
- Oct 2025ISO/IEC 27701:2025
The privacy extension is updated.
- Oct 202827701 transition ends
Certificates to the 2019 edition move to 2025.
[isms_timeline layout="horizontal"]
2013 | ISO/IEC 27001:2013 | Annex A: 114 controls.
Oct 2022 | ISO/IEC 27001:2022 | Annex A: 93 controls in four themes, 11 of them new.
Oct 2025 | ISO/IEC 27701:2025 | The privacy extension is updated.
Oct 2028 | 27701 transition ends | Certificates to the 2019 edition move to 2025.
[/isms_timeline]
Data and proof
Stats grid
Two to four large numbers with a label and a note that count up when scrolled into view. Only verified figures.
[isms_stats count_up="1"]
93 | Annex A controls | ISO/IEC 27001:2022
4 | Control themes | organisational, people, physical, technological
11 | New controls | introduced in the 2022 revision
[/isms_stats]
Editable fields: inner content: Stats: value | label | note (one per line); count_up Animate numbers (default on); style Style — plain, cards (default plain).
Variant: style=”cards”
[isms_stats style="cards" count_up="1"]
37 | Organisational controls
34 | Technological controls
14 | Physical controls
[/isms_stats]
Bar chart
A horizontal bar chart with values, notes and a source line, for comparing counts such as controls per theme.
[isms_bar_chart heading="Annex A controls by theme" source="Source: ISMS.online, Annex A controls (ISO/IEC 27001:2022)"]
Organisational | 37 | 5.1–5.37
Technological | 34 | 8.1–8.34
Physical | 14 | 7.1–7.14
People | 8 | 6.1–6.8
[/isms_bar_chart]
Editable fields: heading Chart title; inner content: Bars: label | value | note (one per line; value numeric); unit Unit suffix (e.g. %); max Scale maximum (0 = auto); highlight_first Highlight the first bar (default on); source Source note.
Line chart
A line chart drawn in the browser from label and value rows, for change over time; readers without JavaScript see a table.
| Label | Value |
|---|---|
| Q1 | 12 |
| Q2 | 9 |
| Q3 | 6 |
| Q4 | 4 |
Example values for layout only, not a real audit history
[isms_line_chart heading="Open nonconformities per quarter (example values)" source="Example values for layout only, not a real audit history"]
Q1 | 12
Q2 | 9
Q3 | 6
Q4 | 4
[/isms_line_chart]
Editable fields: heading Chart title; unit Unit suffix; source Source note; inner content: Points: label | value (one per line); label_header Table header shown without JavaScript (default Label); value_header Table header shown without JavaScript (default Value).
Stacked bar
One bar showing how a total splits into parts, with a legend and percentages, such as new controls by theme.
[isms_stacked_bar heading="The 11 new controls in ISO/IEC 27001:2022, by theme" source="Source: ISMS.online, Annex A controls (ISO/IEC 27001:2022)"]
Organisational | 3
Physical | 1
Technological | 7
[/isms_stacked_bar]
Editable fields: heading Heading; unit Unit suffix; source Source note; inner content: Segments: label | value (one per line).
Percentage rings
Donut rings showing each part’s share of a total, for proportions such as themes within Annex A.
Share of the 93 Annex A controls
- Organisational37 of 93
- Technological34 of 93
- Physical14 of 93
- People8 of 93
[isms_rings heading="Share of the 93 Annex A controls" max="93"]
37 | Organisational | 37 of 93
34 | Technological | 34 of 93
14 | Physical | 14 of 93
8 | People | 8 of 93
[/isms_rings]
Editable fields: heading Heading (optional); max Total (0 = values are percentages); inner content: Rings: value | label | note (one per line).
Progress bars
Percentage bars with the label and value on one line, for implementation or readiness progress. Label example values as examples.
Implementation progress (example values)
- Organisational controls80%
- Technological controls55%
- Physical controls30%site survey booked
[isms_progress heading="Implementation progress (example values)"]
Organisational controls | 80
Technological controls | 55
Physical controls | 30 | site survey booked
[/isms_progress]
Editable fields: heading Heading (optional); inner content: Bars: label | percent | note (one per line).
Trust bar
A label, a row of names or logos and an optional rating chip. Only real, sourced ratings.
[isms_trust_bar label="Frameworks on the platform"]
ISO 27001
ISO 42001
SOC 2
NIS 2
GDPR
[/isms_trust_bar]
Editable fields: label Label; inner content: Names (one per line; “media:123” for a logo); rating Rating (only a real, sourced one); rating_note Rating note / source.
Trust strip
A dark band of short credibility points or standards, usually placed under a page introduction.
Standards referenced on this page
- ISO/IEC 27001:2022
- ISO/IEC 27002:2022
- ISO/IEC 27005
- ISO/IEC 42001:2023
[isms_trust_strip heading="Standards referenced on this page"]
ISO/IEC 27001:2022
ISO/IEC 27002:2022
ISO/IEC 27005
ISO/IEC 42001:2023
[/isms_trust_strip]
Editable fields: heading Heading (optional); inner content: Proof points (one per line; “media:123” for a logo).
Interactive
Tabs
Accessible tabs that switch between short panels (arrow keys, Home, End); without JavaScript every panel is shown.
Stage 1
A documentation review: scope, policy, risk assessment and the Statement of Applicability.
Stage 2
An implementation audit: the auditor tests whether the ISMS works as documented.
Surveillance
Periodic audits between certification and recertification.
[isms_tabs]
Stage 1 | A documentation review: scope, policy, risk assessment and the Statement of Applicability.
Stage 2 | An implementation audit: the auditor tests whether the ISMS works as documented.
Surveillance | Periodic audits between certification and recertification.
[/isms_tabs]
Editable fields: inner content: Tabs: label | text (one per line).
Accordion
Expandable sections, optionally one open at a time, for long detail readers can open on demand. Adds no FAQ schema.
Organisational controls (5.1–5.37)
37 controls, from policies to supplier relationships and incident management.
People controls (6.1–6.8)
8 controls, from screening to remote working.
Physical controls (7.1–7.14)
14 controls, from perimeters to equipment disposal.
[isms_accordion exclusive="1"]
Organisational controls (5.1–5.37) | 37 controls, from policies to supplier relationships and incident management.
People controls (6.1–6.8) | 8 controls, from screening to remote working.
Physical controls (7.1–7.14) | 14 controls, from perimeters to equipment disposal.
[/isms_accordion]
Editable fields: inner content: Sections: title | text (one per line); open Open on load — none, first, all (default first); exclusive Only one section open at a time (default off).
FAQ accordion
Questions and answers with FAQPage structured data, optional category filters and one answer open at a time.
FAQs
How many controls are in Annex A of ISO 27001:2022?
93, grouped into four themes: organisational (37), people (8), physical (14) and technological (34).
What changed from the 2013 version?
Annex A controls were condensed from 114 to 93, regrouped into four themes, and 11 controls are new.
Where are the requirements an auditor checks?
In clauses 4 to 10 of the standard. Annex A is the reference control set the Statement of Applicability is built from.
[isms_faq heading="FAQs" open="1"]
How many controls are in Annex A of ISO 27001:2022? | 93, grouped into four themes: organisational (37), people (8), physical (14) and technological (34). | Annex A
What changed from the 2013 version? | Annex A controls were condensed from 114 to 93, regrouped into four themes, and 11 controls are new. | Annex A
Where are the requirements an auditor checks? | In clauses 4 to 10 of the standard. Annex A is the reference control set the Statement of Applicability is built from. | Requirements
[/isms_faq]
Editable fields: heading Heading (optional) (default FAQs); inner content: Questions: question | answer | category (one per line); schema Output FAQPage schema (default on); open First item open by default (default off); single One answer open at a time (default on); all_label Label of the show-all category filter (default All).
On this page
A contents list built from the page’s H2 headings, or from explicit links, for long guides without the sidebar.
[isms_toc]Editable fields: heading Heading (default On this page); inner content: Optional links: label | #anchor (one per line).
Card slider
Editorial story tiles on a scroll-snap track with previous and next buttons, for a short series of related guides.
[isms_slider heading="ISO 27001 guides"]
Annex A explained | The 93 controls in four themes. | Guide | https://www.isms.online/iso-27001/annex-a-2022/ | | ISO 27001
Requirements and clauses | Clauses 4 to 10, one by one. | Guide | https://www.isms.online/iso-27001/requirements-2022/ | | ISO 27001
Statement of Applicability | What goes in it and why. | Guide | https://www.isms.online/iso-27001/statement-of-applicability/ | | ISO 27001
Certification | Stage 1, stage 2 and surveillance. | Guide | https://www.isms.online/iso-27001/certification/ | | ISO 27001
[/isms_slider]
Editable fields: heading Heading (optional); inner content: Tiles: title | text | kicker | url | image URL | meta (one per line); of_label Tile counter wording: “1 of 4” (default of).
Media, links and resources
Figure with caption
An image with caption and credit from the media library or a URL; with no image it shows a placeholder box.
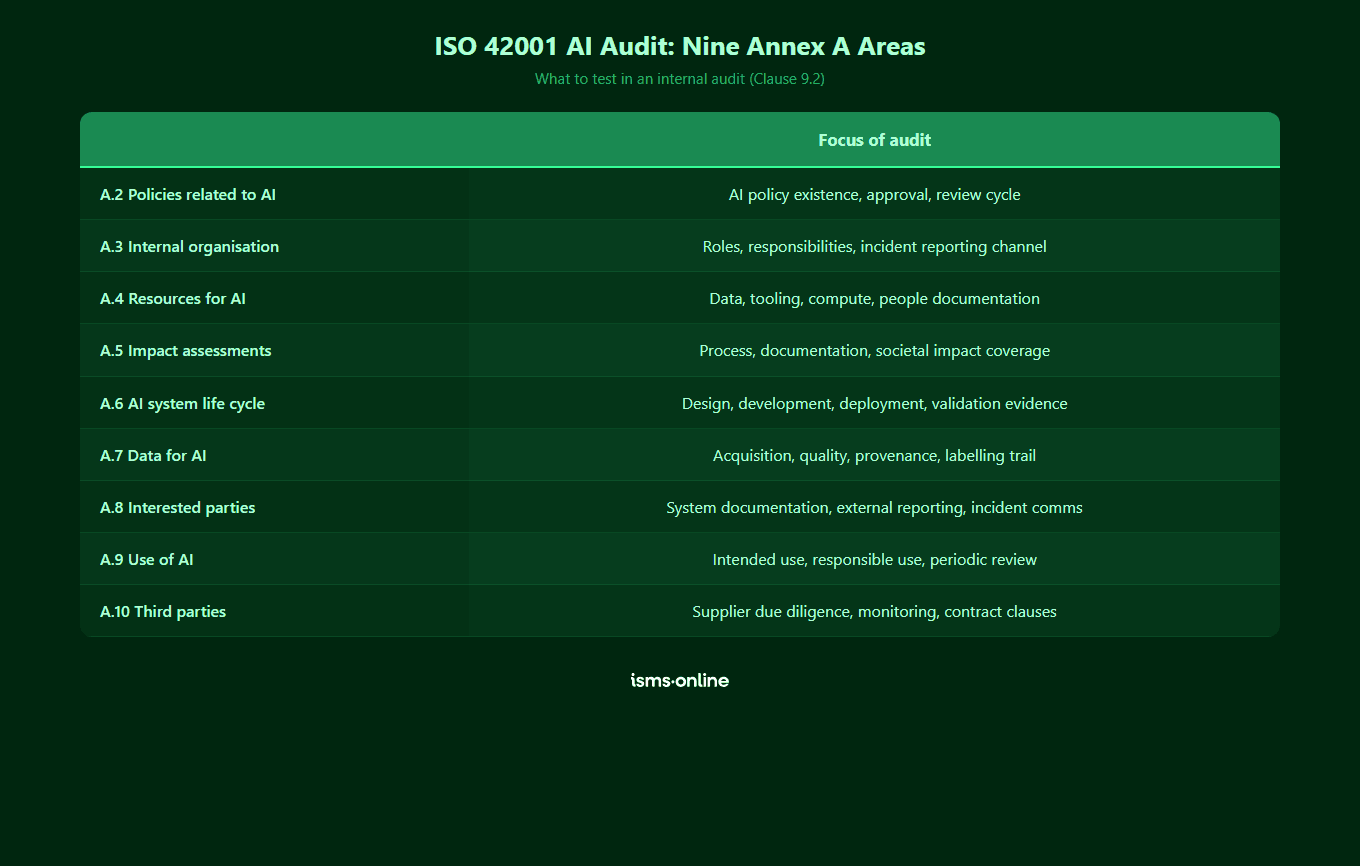
[isms_figure src="https://www.isms.online/app/uploads/2026/04/ai-audit-checklist-nine-annex-a-areas-2026.png" alt="ISO 42001 AI audit checklist covering the nine Annex A control areas, A.2 to A.10" credit="ISMS.online"]
The nine Annex A control areas of ISO/IEC 42001, from the ISO 42001 AI audit checklist.
[/isms_figure]
Editable fields: src Image URL; media Image (media ID, overrides the URL); alt Alt text; inner content: Caption; credit Credit (optional); credit_url Credit URL; placeholder Placeholder text when there is no image or alt text (default Image placeholder).
Variant: no image (placeholder)
[isms_figure alt="Screenshot placeholder: risk register view"]Video (click to load)
A Vimeo or YouTube video that loads nothing from the provider until the reader clicks play.
[isms_video provider="vimeo" id="879357671" title="So you need to get ISO 27001 certified?"]
ISMS.online video, also used on the ISO 27001 guide pages.
[/isms_video]
Editable fields: provider Provider — vimeo, youtube (default vimeo); id Video ID; title Video title; inner content: Caption (optional); play_label Play button label (default Play video).
Artefact previews
Cards naming a document with a small drawn preview (document, table, bars or map), for showing what an ISMS produces.
- Statement of ApplicabilityStatement of ApplicabilityEvery control, included or excluded, with the reason.
- Risk treatmentRisk treatment planOwners, options and due dates per risk.
- PolicyInformation security policyApproved by top management (clause 5.2).
[isms_artefacts]
table | Statement of Applicability | Statement of Applicability | Every control, included or excluded, with the reason.
bars | Risk treatment | Risk treatment plan | Owners, options and due dates per risk.
doc | Policy | Information security policy | Approved by top management (clause 5.2).
[/isms_artefacts]
Editable fields: inner content: Artefacts: preview | tag | title | text (preview = doc, table, bars, map).
Resource card
A guide, checklist or template with an icon, description and button, for pointing to one next resource.
GuideWeb page
ISO 27001: the ultimate guide
Clauses, Annex A, certification and the Statement of Applicability in one place.
[isms_resource kind="Guide" title="ISO 27001: the ultimate guide" url="https://www.isms.online/iso-27001/" format="Web page" button_label="Read the guide"]
Clauses, Annex A, certification and the Statement of Applicability in one place.
[/isms_resource]
Editable fields: kind Kind (Guide, Checklist, Template…) (default Guide); title Title; inner content: Description; url URL; format Format (e.g. PDF, web page); button_label Button label (default Open).
Related links
Cross-link cards, compact rows or image cards pointing to related pages, usually at the end of a section.
[isms_related]
ISO 42001 vs ISO 27001 | https://www.isms.online/iso-42001/vs-iso-27001/ | How the AI and information security standards fit together.
Statement of Applicability | https://www.isms.online/iso-27001/statement-of-applicability/ | What goes in it, and why each control is there.
ISO 27001 certification | https://www.isms.online/iso-27001/certification/ | Stage 1, stage 2 and surveillance audits.
[/isms_related]
Editable fields: heading Heading (optional); inner content: Links: title | url | text | tag | image URL (one per line); style Style — pairs, list, blog (default pairs).
Variant: style=”list”
[isms_related style="list" heading="Related reading"]
Annex A explained | https://www.isms.online/iso-27001/annex-a-2022/
Requirements and clauses | https://www.isms.online/iso-27001/requirements-2022/
[/isms_related]
Variant: style=”blog”
[isms_related style="blog"]
The 93 Annex A controls, explained | https://www.isms.online/iso-27001/annex-a-2022/ | | Annex A
ISO 27001 clauses 4 to 10 | https://www.isms.online/iso-27001/requirements-2022/ | | Requirements
ISO 42001 vs ISO 27001 | https://www.isms.online/iso-42001/vs-iso-27001/ | | Comparison
[/isms_related]
Card grid
A grid of cards with kicker, title, text and a link, in door, proof or pain tones, for entry points or symptoms.
[isms_cards tone="door" columns="3"]
Annex A explained | The 93 controls in four themes. | https://www.isms.online/iso-27001/annex-a-2022/ | Controls
Requirements | Clauses 4 to 10, one by one. | https://www.isms.online/iso-27001/requirements-2022/ | Clauses
Certification | Stage 1, stage 2 and surveillance. | https://www.isms.online/iso-27001/certification/ | Audits
[/isms_cards]
Editable fields: heading Heading (optional); inner content: Cards: title | text | url | kicker (one per line); tone Tone — default, proof, pain, door (default default); columns Columns (2-4) (default 3); link_label Link label on cards with a URL (default Explore).
Variant: tone=”pain” columns=”2″
Controls picked from a list
Annex A copied in full, with no link to the risk assessment.
Exclusions without reasons
The Statement of Applicability leaves out why a control does not apply.
[isms_cards tone="pain" columns="2"]
Controls picked from a list | Annex A copied in full, with no link to the risk assessment.
Exclusions without reasons | The Statement of Applicability leaves out why a control does not apply.
[/isms_cards]
Case-study cards
Colour-blocked cards with a headline and one stat per customer story. Only real, signed-off numbers.
- Demo · FinancePlaceholder case study headline[ — ]signed-off metric
- Demo · HealthcarePlaceholder case study headline[ — ]signed-off metric
- Demo · SaaSPlaceholder case study headline[ — ]signed-off metric
[isms_case_cards]
Demo · Finance | Placeholder case study headline | [ — ] | signed-off metric
Demo · Healthcare | Placeholder case study headline | [ — ] | signed-off metric
Demo · SaaS | Placeholder case study headline | [ — ] | signed-off metric
[/isms_case_cards]
Editable fields: inner content: Cards: kicker | title | stat | stat label | url (one per line).
Feature grid
An icon, title and line as cards, deliverable rows or proof points, for what an ISMS covers or what is included.
- PoliciesWhat the organisation commits to.
- PeopleScreening, awareness and responsibilities.
- AccessWho can reach which information.
[isms_feature_grid]
doc | Policies | What the organisation commits to.
users | People | Screening, awareness and responsibilities.
lock | Access | Who can reach which information.
[/isms_feature_grid]
Editable fields: columns Columns (2-4) (default 3); style Style — cards, rows, proof (default cards); inner content: Features: icon | title | text (one per line).
Variant: style=”rows” columns=”2″
- Risk treatment planOwners and due dates per risk.
- Statement of ApplicabilityEvery control and its justification.
- Internal audit reportFindings against clauses 4 to 10.
- Management review minutesDecisions and actions (clause 9.3).
[isms_feature_grid style="rows" columns="2"]
shield | Risk treatment plan | Owners and due dates per risk.
doc | Statement of Applicability | Every control and its justification.
search | Internal audit report | Findings against clauses 4 to 10.
chart | Management review minutes | Decisions and actions (clause 9.3).
[/isms_feature_grid]
Variant: style=”proof”
- Physical14 controls, 7.1–7.14.
- Technological34 controls, 8.1–8.34.
- People8 controls, 6.1–6.8.
- Organisational37 controls, 5.1–5.37.
- New in 202211 controls.
- Four themesReplacing 14 domains.
[isms_feature_grid style="proof"]
building | Physical | 14 controls, 7.1–7.14.
server | Technological | 34 controls, 8.1–8.34.
users | People | 8 controls, 6.1–6.8.
doc | Organisational | 37 controls, 5.1–5.37.
alert | New in 2022 | 11 controls.
globe | Four themes | Replacing 14 domains.
[/isms_feature_grid]
Breadcrumbs
A Home / section / page trail, built from the page’s ancestors when no items are given. Learn pages already show one in the hero.
[isms_breadcrumbs]
Home | /
ISO 27001 | /iso-27001/
Annex A explained
[/isms_breadcrumbs]
Editable fields: inner content: Crumbs: label | url (one per line; empty = automatic).
Pagination
Previous and next links with numbered pages, for a series such as clause-by-clause guides.
[isms_pager prev_label="Clause 9.1" prev_url="/iso-27001/requirements-2022/how-to-implement-iso-27001-2022-clause-9-1-monitoring-measurement-analysis-and-evaluation/" next_label="Clause 9.3" next_url="/iso-27001/requirements-2022/how-to-implement-iso-27001-2022-clause-9-3-management-review/"]
9.1 | /iso-27001/requirements-2022/how-to-implement-iso-27001-2022-clause-9-1-monitoring-measurement-analysis-and-evaluation/
9.2 | /iso-27001/requirements-2022/how-to-implement-iso-27001-2022-clause-9-2-internal-audit/ | 1
9.3 | /iso-27001/requirements-2022/how-to-implement-iso-27001-2022-clause-9-3-management-review/
[/isms_pager]
Editable fields: inner content: Pages: label | url | current (one per line; current = 1); prev_label Previous label; prev_url Previous URL; next_label Next label; next_url Next URL; prev_text Small label above the previous link (default Previous); next_text Small label above the next link (default Next).
Calls to action
Buttons
A row of buttons: mint for conversion, blue for actions, ghost, dark and text styles.
[isms_buttons]
Book a demo | /book-a-demo/ | primary
Read the guide | /iso-27001/ | action
See Annex A | /iso-27001/annex-a-2022/ | ghost
Certification | /iso-27001/certification/ | dark
[/isms_buttons]
Editable fields: inner content: Buttons: label | url | style (primary, action, ghost, dark, text); size Size — md, sm (default md); arrow Arrow on primary and action buttons (default on).
Soft CTA strip
An eyebrow, heading and short text level with one or two buttons, for readers not ready to book a demo.
Not ready to talk?
Start with the ISO 27001 guide
Clauses, Annex A and certification, explained in plain English.
[isms_cta_strip eyebrow="Not ready to talk?" heading="Start with the ISO 27001 guide" button_label="Read the guide" button_url="/iso-27001/" secondary_label="Book a demo" secondary_url="/book-a-demo/"]
Clauses, Annex A and certification, explained in plain English.
[/isms_cta_strip]
Editable fields: eyebrow Eyebrow (optional); heading Heading (optional); inner content: Text; button_label Button label (default Book a demo); button_url Button URL (default /book-a-demo/); secondary_label Secondary button label (optional); secondary_url Secondary button URL.
Final CTA band
A decisive moss band, centred, with one primary action and an optional second, placed at the end of a page.
Next step
See an ISMS built around the 2022 control set
A walkthrough of scope, risk, the Statement of Applicability and the audit trail.
[isms_cta_band heading="See an ISMS built around the 2022 control set" secondary_label="ISO 27001 guide" secondary_url="/iso-27001/"]
A walkthrough of scope, risk, the Statement of Applicability and the audit trail.
[/isms_cta_band]
Editable fields: layout Layout — center, left (default center); eyebrow Eyebrow (default Next step); heading Heading; inner content: Text; primary_label Primary button label (default Book a demo); primary_url Primary button URL (default /book-a-demo/); secondary_label Secondary button label (optional); secondary_url Secondary button URL.
Sticky CTA bar
A bottom bar that appears after the reader scrolls and can be dismissed for the session. One per page at most.
[isms_sticky_bar text="See ISMS.online in action" subtext="Demo element: a sticky call-to-action bar" secondary_label="ISO 27001 guide" secondary_url="/iso-27001/"]Editable fields: inner content: Text; subtext Secondary line (optional); button_label Button label (default Book a demo); button_url Button URL (default /book-a-demo/); secondary_label Secondary button label (optional); secondary_url Secondary button URL; show_after Show after scrolling (px) (default 600).
Site shortcodes
Shortcodes provided by the ISMS.online theme, used across the ISO 27001 and ISO 42001 pages. They sit alongside the elements above.
Pull quote (theme)
The standard pull quote on ISO 27001 and ISO 42001 learn pages: plain text in the blockquote attribute, with optional author and role. Use it for one line worth repeating. Shortcode: [single_quote].
Scope it honestly, assess the risk, then choose the control.
- Demo attribution, Role
[single_quote blockquote="Scope it honestly, assess the risk, then choose the control." author="Demo attribution" role="Role"]Highlight block (theme)
A tinted box with a title, a short description and an optional button, used on learn pages to push a next step such as booking a demo. Shortcode: [custom_highlight_block].
[custom_highlight_block title="Book a demo" description="See how the 93 Annex A controls map to your ISMS." show_button="true" button_text="Book a demo" button_url="/book-a-demo/"][/custom_highlight_block]Reusable CTA (theme)
Inserts a CTA post by its slug; learn pages usually carry three. Its heading is kept out of “Jump to topic”. Shortcode: [io_cta].
Everything you need for ISO 42001
Structured content, mapped risks and built-in workflows to help you govern AI responsibly and with confidence.
[io_cta id="lf-cta-iso-42001"]Static block (theme)
Inserts a reusable static block by slug, for example the ISO 42001 requirements table shared across pages. Shortcode: [io_static_block].
| ISO 42001 Requirement | ISO 42001 Requirement Name |
|---|---|
| ISO 42001 Requirement 1 | Scope |
| ISO 42001 Requirement 2 | Normative References |
| ISO 42001 Requirement 3 | Terms and Definitions |
| ISO 42001 Requirement 4 | Context of the Organisation |
| ISO 42001 Requirement 5 | Leadership |
| ISO 42001 Requirement 6 | Planning |
| ISO 42001 Requirement 7 | Support |
| ISO 42001 Requirement 8 | Operation |
| ISO 42001 Requirement 9 | Performance Evaluation |
| ISO 42001 Requirement 10 | Improvement |
[io_static_block id="iso-42001-requirements-table"]Button (theme)
A single theme button with text, URL and type (mint, black, white or the transparent and text-only variants). Shortcode: [button].
[button text="Book a demo" url="/book-a-demo/" type="black"]Accordion (theme)
The theme’s accordion: an accordion_block with accordion_item children, each a title and HTML body. Shortcode: [accordion_block].
Annex A themes
Organisational
37 controls, 5.1–5.37.
People
8 controls, 6.1–6.8.
[accordion_block title="Annex A themes"]
[accordion_item title="Organisational"]<p>37 controls, 5.1–5.37.</p>[/accordion_item]
[accordion_item title="People"]<p>8 controls, 6.1–6.8.</p>[/accordion_item]
[/accordion_block]
Columns (theme)
Places content side by side; each col takes a fractional width such as 1/2 or 1/3. Shortcode: [columns].
Clauses 4 to 10 hold the requirements.
Annex A holds the 93 reference controls.
[columns gap="2rem" valign="center"]
[col width="1/2"]<p>Clauses 4 to 10 hold the requirements.</p>[/col]
[col width="1/2"]<p>Annex A holds the 93 reference controls.</p>[/col]
[/columns]
Lead paragraph (theme)
A larger introductory paragraph for the start of a section. Shortcode: [lead].
A lead paragraph sets up a section in a larger size.
[lead]A lead paragraph sets up a section in a larger size.[/lead]Blockquote (theme)
A blockquote with the quote between the tags and an author and role underneath. Shortcode: [io_quote].
“Demo quote: replace with a real, attributable line.”
Role
[io_quote author="Demo attribution" role="Role"]Demo quote: replace with a real, attributable line.[/io_quote]G2 badges (theme)
The row of G2 award badges maintained by the theme. Shortcode: [g2_badges].



[g2_badges]Case study slider (theme)
A slider of real ISMS.online customer case studies; max limits how many are shown. Shortcode: [case_study_slider].

How Blue Services Achieved Triple ISO Certification Success
Blue Services needed external support to guide them through ISO 27001, ISO 9001 and ISO 14001 implementation and best practices, and a platform to centralise their overall compliance management.

How Evolution Funding Cruised to ISO 27001 Certification Success
Achieving ISO 27001 certification was a core objective for Evolution Funding. The team needed a centralised platform with which they could implement the ISO 27001 standard and work through the compliance process.
How 4way Consulting Paved the Road to ISO 27001 Success
Handling sensitive client data across multiple standards, 4way needed a cost and time-efficient way to pursue ISO 27001 – without building an ISMS from scratch or relying on expensive external consultants.
[case_study_slider max="3"]Section divider (theme)
The short rule between content blocks on every learn page; one follows each section on this page. Shortcode: [spacer].
[spacer]Interactive tools
Calculators, quizzes and explorers (risk matrix, Annex A explorer, readiness and awareness quizzes, 2022 transition checker) are a separate plugin. See them working on the interactive tools page; each is placed with one shortcode, for example:
[isms-tool type="risk-matrix"]